ARP Certificate Network Security Credentials for IT Professionals

ARP Certificate

Network Security Credentials for IT Professionals

Latest Articles

Anatomy of a Supply Chain Breach: How Gratuitous ARP Manipulation Enabled Persistent Network Access Across a Manufacturing Environment
Network Security

Anatomy of a Supply Chain Breach: How Gratuitous ARP Manipulation Enabled Persistent Network Access Across a Manufacturing Environment

A fictionalized but technically accurate forensic case study reconstructs how an attacker exploited gratuitous ARP behavior to achieve persistent lateral movement within a manufacturing supply chain network. The analysis details each phase of the attack, the detection failures that allowed it to persist, and the specific defensive controls that could have interrupted the intrusion chain.
Depth Over Breadth: Why ARP-Specific Credentials Are Outperforming General Security Certifications in Layer 2 Hiring Decisions
Career Development

Depth Over Breadth: Why ARP-Specific Credentials Are Outperforming General Security Certifications in Layer 2 Hiring Decisions

Traditional security certifications leave dangerous gaps when it comes to Layer 2 protocol expertise, and hiring managers are noticing. This comparative analysis examines why ARP-focused credentials are increasingly decisive in technical security roles and how IT professionals can make smarter credentialing decisions in a competitive market.

Alert Fatigue Is Winning: How Misconfigured ARP Detection Rules Are Blinding Your Security Team to Real Threats
Network Security

Alert Fatigue Is Winning: How Misconfigured ARP Detection Rules Are Blinding Your Security Team to Real Threats

ARP monitoring systems generate some of the highest alert volumes in enterprise security operations—yet most of that volume is noise. When detection rules are poorly tuned, analysts stop trusting the data, and genuine attacks pass through uncontested. This article examines the structural misconfigurations driving ARP alert fatigue and offers a practical framework for restoring signal integrity in production environments.

Kubernetes and the ARP Security Gap: Why Container Networking Has Outpaced the Tools Designed to Protect It
Network Security

Kubernetes and the ARP Security Gap: Why Container Networking Has Outpaced the Tools Designed to Protect It

Containerized infrastructure has fundamentally altered the Layer 2 attack surface in ways that traditional ARP security tooling was never designed to address. Kubernetes networking models introduce ARP behaviors that legacy intrusion detection systems cannot interpret accurately, leaving security teams with visibility gaps they may not know exist. This article examines the specific ARP vulnerabilities that emerge in container orchestration environments and the detection strategies capable of add

Elevating Your Market Value in 2025: The Protocol-Level Network Security Expertise That Moves SOC Analysts Into Specialist Roles
Career Development

Elevating Your Market Value in 2025: The Protocol-Level Network Security Expertise That Moves SOC Analysts Into Specialist Roles

The path from SOC analyst to network security specialist is well traveled but rarely well mapped. In 2025, employers are drawing a sharper distinction between analysts who can operate security tools and those who understand the protocols those tools are monitoring. ARP expertise has emerged as a concrete differentiator—one that influences hiring decisions, compensation negotiations, and long-term career trajectory in measurable ways.

Your First ARP Lab Will Break — Here Is Exactly Why and How to Rebuild It Correctly
Network Security

Your First ARP Lab Will Break — Here Is Exactly Why and How to Rebuild It Correctly

Most IT professionals underestimate how many configuration pitfalls await them in their first ARP lab environment. From misconfigured packet captures to incorrect VLAN assignments, the early failures are predictable — and entirely fixable. This guide walks certification candidates through the most common setup errors and the precise steps needed to correct them before exam day.

Vendor-Shipped ARP Flaws: A Procurement Audit Framework for Security Teams Who Cannot Afford to Assume Compliance
Network Security

Vendor-Shipped ARP Flaws: A Procurement Audit Framework for Security Teams Who Cannot Afford to Assume Compliance

Enterprise network equipment has shipped from major vendors with documented ARP implementation flaws that persisted undetected through deployment and into production. Security teams that rely on vendor reputation rather than protocol-level verification are accepting risk they may not be able to quantify. This article outlines a structured audit approach for evaluating third-party equipment before it reaches your infrastructure.

Why the Security Job Market Is Rewarding Protocol Depth Over Broad Certification Portfolios
Career Development

Why the Security Job Market Is Rewarding Protocol Depth Over Broad Certification Portfolios

The security hiring landscape is undergoing a measurable shift away from candidates who hold multiple general-purpose certifications toward those who demonstrate deep, verifiable expertise at the protocol level. Analysis of current job postings and feedback from hiring managers suggests that specialized Layer 2 knowledge — including ARP — has become a genuine differentiator in mid-to-senior security roles. This article examines why that shift is happening and what it means for your career strate

Reading the Past From ARP Logs: A Forensic Analyst's Guide to Reconstructing Network Events After the Fact
Network Security

Reading the Past From ARP Logs: A Forensic Analyst's Guide to Reconstructing Network Events After the Fact

When conventional network telemetry is absent, corrupted, or deliberately erased, ARP logs and cache artifacts frequently contain the residual evidence that makes incident reconstruction possible. For forensic analysts and incident responders who know how to read them, these records can establish attack timelines, identify spoofing activity, and produce evidence chains that withstand scrutiny in post-incident reviews. This guide provides a structured framework for extracting that intelligence wh

How Hybrid Infrastructure Breaks Layer 2 Security — And What ARP Exposes When It Does
Network Security

How Hybrid Infrastructure Breaks Layer 2 Security — And What ARP Exposes When It Does

Hybrid deployments — spanning on-premises switching infrastructure, cloud virtual networks, and edge computing nodes — introduce ARP attack surfaces that conventional segmentation strategies were never designed to address. As enterprise architectures grow more distributed, the assumptions embedded in traditional Layer 2 security controls become liabilities rather than protections. This technical examination walks through the architectural patterns, threat scenarios, and validation techniques tha

What Hiring Managers Actually Test For in Entry-Level Security Roles — And Why Your ARP Credentials May Not Be Enough
Career Development

What Hiring Managers Actually Test For in Entry-Level Security Roles — And Why Your ARP Credentials May Not Be Enough

Passing a certification exam and performing effectively in a first security role are two experiences that rarely overlap as neatly as candidates expect. A growing number of hiring managers report that entry-level applicants with ARP-related credentials still arrive unprepared for the operational realities of the job. Understanding where that gap originates — and how to close it before the interview — is increasingly the difference between an offer and a rejection.

The Layer 2 Blind Spot That Most Penetration Tests Never Reach — And What Attackers Do With It
Network Security

The Layer 2 Blind Spot That Most Penetration Tests Never Reach — And What Attackers Do With It

Most penetration testing engagements stop well short of the protocol layer where ARP vulnerabilities live, leaving organizations with a false sense of validated security. Attackers who understand Layer 2 mechanics exploit precisely the gaps that standard pen test methodologies overlook. Security teams that fail to demand protocol-level testing are, in effect, auditing only half of their attack surface.

The Compliance Blind Spot Hiding in Plain Sight: Why Auditors Must Start Taking ARP Seriously
Network Security

The Compliance Blind Spot Hiding in Plain Sight: Why Auditors Must Start Taking ARP Seriously

SOC 2, ISO 27001, and HIPAA have long concentrated their scrutiny on Layer 3 and above, leaving Address Resolution Protocol largely untouched by formal audit processes. This oversight creates measurable vulnerabilities in enterprise compliance posture that adversaries are well-positioned to exploit. Understanding why ARP falls through the regulatory cracks—and how to close that gap—is now a professional imperative for IT security teams.

Why Self-Study Leaves ARP Knowledge Fragmented — And What Structured Credentialing Actually Fixes
Career Development

Why Self-Study Leaves ARP Knowledge Fragmented — And What Structured Credentialing Actually Fixes

For many IT professionals, self-directed study of Address Resolution Protocol produces surface-level familiarity rather than deployable expertise — a distinction that quietly stalls promotions and undermines salary negotiations. Structured certification programs close that gap by building systematic, verifiable competency that employers can evaluate at a glance. This article examines why the difference matters, and what real career trajectories reveal about the cost of skipping formal credential

When Segmentation Fails Silently: How ARP Behavior Exposes the Gaps in Your Subnet Isolation Strategy
Network Security

When Segmentation Fails Silently: How ARP Behavior Exposes the Gaps in Your Subnet Isolation Strategy

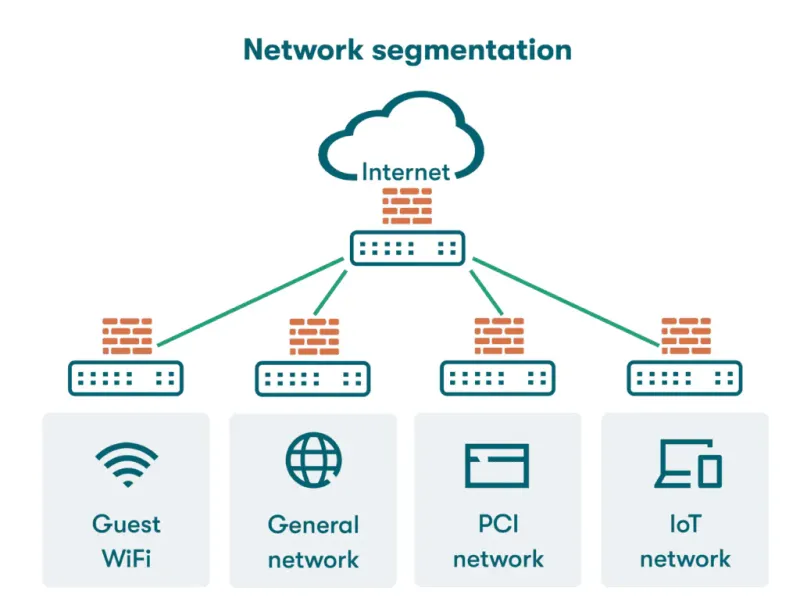
Organizations frequently invest significant resources in network segmentation, only to find that ARP traffic quietly crosses boundaries they assumed were secure. This article examines how misconfigured ARP behavior at Layer 2 undermines subnet isolation, why compliance frameworks rarely catch these gaps, and what IT security professionals must do to diagnose and remediate them before attackers exploit the exposure.

The ARP Proxy Problem: How Flawed Assumptions Are Quietly Undermining Enterprise Network Architecture
Network Security

The ARP Proxy Problem: How Flawed Assumptions Are Quietly Undermining Enterprise Network Architecture

ARP proxy is one of the most misunderstood mechanisms in enterprise networking, and the consequences of that misunderstanding extend far beyond misconfiguration. Security teams operating in hybrid and multi-subnet environments routinely make architectural decisions based on assumptions about ARP proxy behavior that simply do not hold under real-world conditions. This article examines the gap between perceived and actual ARP proxy behavior—and what correcting that gap means for your network's sec

Zero-Trust Has a Layer 2 Blind Spot — And ARP Is Standing Right in It
Network Security

Zero-Trust Has a Layer 2 Blind Spot — And ARP Is Standing Right in It

Zero-trust architecture has reshaped how enterprises think about access control and identity verification, yet most implementations stop short of addressing ARP at the protocol level. This gap leaves Layer 2 environments exposed even when Layer 3 and above appear tightly governed. Understanding where ARP fits within microsegmentation policy is no longer optional for organizations pursuing NIST or CIS compliance.

Why Your On-Premises ARP Playbook Breaks Down the Moment You Move to the Cloud
Network Security

Why Your On-Premises ARP Playbook Breaks Down the Moment You Move to the Cloud

Security teams that built rigorous ARP defenses for physical networks are discovering those controls offer little protection once workloads migrate to AWS, Azure, or GCP. The fundamental way each cloud provider handles address resolution diverges sharply from traditional Ethernet behavior, creating blind spots that hybrid environment managers rarely anticipate. This article examines those divergences in detail and outlines provider-specific mitigation strategies that align with modern certificat

Certified But Unprepared: Closing the Gap Between ARP Exam Success and Real-World Incident Response
Career Development

Certified But Unprepared: Closing the Gap Between ARP Exam Success and Real-World Incident Response

Earning an ARP-related certification is a meaningful milestone, but hiring managers and incident responders across the United States are raising a consistent alarm: many certified professionals struggle when actual protocol-level attacks materialize in production environments. This article examines the structural disconnect between what certification curricula test and what enterprise security operations genuinely demand, offering a practical framework for transforming exam-ready knowledge into

Dynamic ARP Inspection Deployments That Keep Failing: A Compliance-Ready Troubleshooting Framework for Security Teams
Network Security

Dynamic ARP Inspection Deployments That Keep Failing: A Compliance-Ready Troubleshooting Framework for Security Teams

Despite widespread awareness of Dynamic ARP Inspection as a critical security control, many organizations discover during audits that their DAI configurations are incomplete, misconfigured, or entirely ineffective in production. This article examines the root causes behind failed ARP inspection rollouts and provides a structured framework security teams can use to validate, correct, and future-proof their implementations before the next compliance review.